 |
| Site Plan New DHS Building |
Since my
original post on the Lockheed Martin / Prime contractors breach which I and other security researchers connected to the EMC RSA breach (a fact that EMC has now
conceded to), I've been investigating possible motives for this multi-faceted attack. Its always been my belief that RSA's technology was not the primary target but a means to an end. And that "end" apparently involved breaching the networks of multiple Department of Defense contractors: Lockheed Martin, L-3 Communications, and allegedly Northrop Grumman. Other primes mentioned as possibilities by Reuters included General Dynamics, Boeing, and Raytheon.
If RSA was stage one of a multi-stage operation, that would suggest that Lockheed, L-3, and Northrup Grumman as the targets would have something else in common besides just being DOD contractors. Since it's my
belief that the EMC RSA attack started earlier than March, 2011 and took some planning prior to its launch, I began looking for contract awards in mid to late 2010 that involved the three victim companies. I found a couple of possibilities that warranted further consideration but then I came across this news item from November 8, 2010:
4 competitors protest award of $2.6 billion IT contract to Northrop GrummanThe award, which is now up for re-bidding (
GSA solicitation GST0011AJ0021) is for the crown jewels of the new Department of Homeland Security headquarters - building the infrastructure which will support information technology, telecommunications, security, and building management systems. The contractors who filed protests with GAO are Lockheed Martin, General Dynamics, Serco and L-3 Communications. Of the five companies involved, Lockheed and L-3 are confirmed attack targets, Northrop is an alleged target and General Dynamics is a possible target. Serco hasn't been named by any sources familiar with this attack but they also don't use RSA SecurID tokens; opting instead for
Signify, one of RSA's competitors for two factor authentication.
In order to compete for an award, companies must submit detailed technical proposals in written and oral form with an accompanying slide deck. DHS' acquisition schedule for the competing vendors corresponds with the known dates of the attacks:
 |
| DHS TIP Industry Day Deck: (Slide 39) |
According to the schedule on slide #39, vendor written proposals were due in April and Orals were due in May. L-3 Communications announced active targeting with penetration attacks on April 6, 2011 while Lockheed reported that its breach commenced on May 21. Late May was also the time of the alleged attack against Northrop Grumman.
The information and communications infrastructure of the new DHS headquarters would certainly be a target of interest for foreign intelligence services like the FSB. Even the technical proposals from competing DOD contractors would contain valuable information. The level of detail asked for by DHS is fairly intensive as evidenced by the following slide which breaks out one of the eight required tasks:
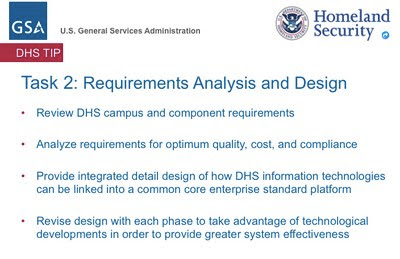 |
| Task 2: Requirements Analysis and Design (slide 26) |
If the November, 2010 article in the Washington Post triggered the planning stage of the operation, it offered sufficient time for an adversary to discover that the vendors shared the same two factor authentication technology; perform social engineering research on the target companies' employees, probe company websites for vulnerabilities, and craft customized attacks if needed. This doesn't require the resources of a nation state. Any experienced Eastern European hacker crew could pull it off with a relatively low budget. The upside however is huge. The information contained in those DHS technical proposals could be sold to multiple foreign governments and net the crew a seven figure or eight figure payday. And considering the scope of the DHS HQ project (the largest federal construction job since the Pentagon was built in the 1940's according to the Washington Post), this probably isn't the end of it. Whichever prime contractor wins the TIP contract, along with its sub-contractors, will almost certainly become the next targets to be compromised.


